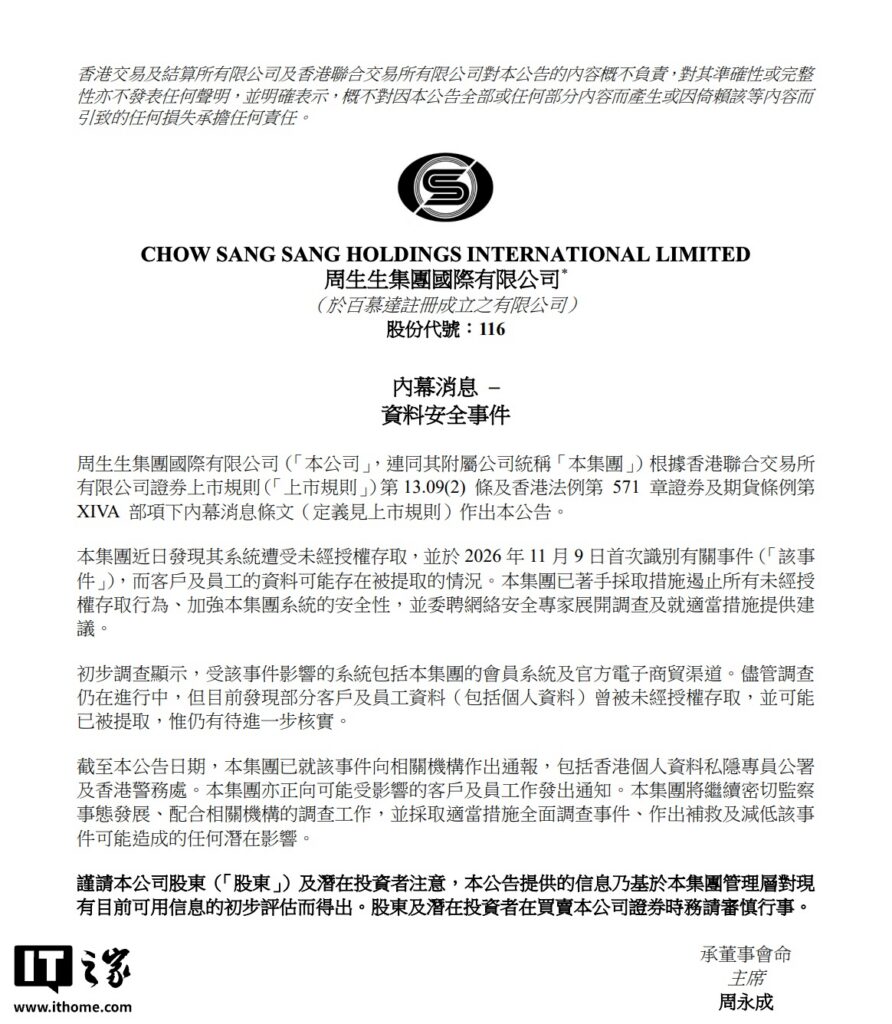
Jewelry retailer Chow Sang Sang said in a November 12, 2026 notice that it had detected unauthorized access to its systems. The group first identified the incident on November 9 and said customer and employee information may have been extracted.
According to the company’s preliminary investigation, the affected systems included its membership system and official e-commerce channels. Some customer and employee data, including personal information, had been accessed without authorization and may have been extracted. The group said it had taken steps to stop the unauthorized access, strengthen system security and engage cybersecurity specialists to investigate.
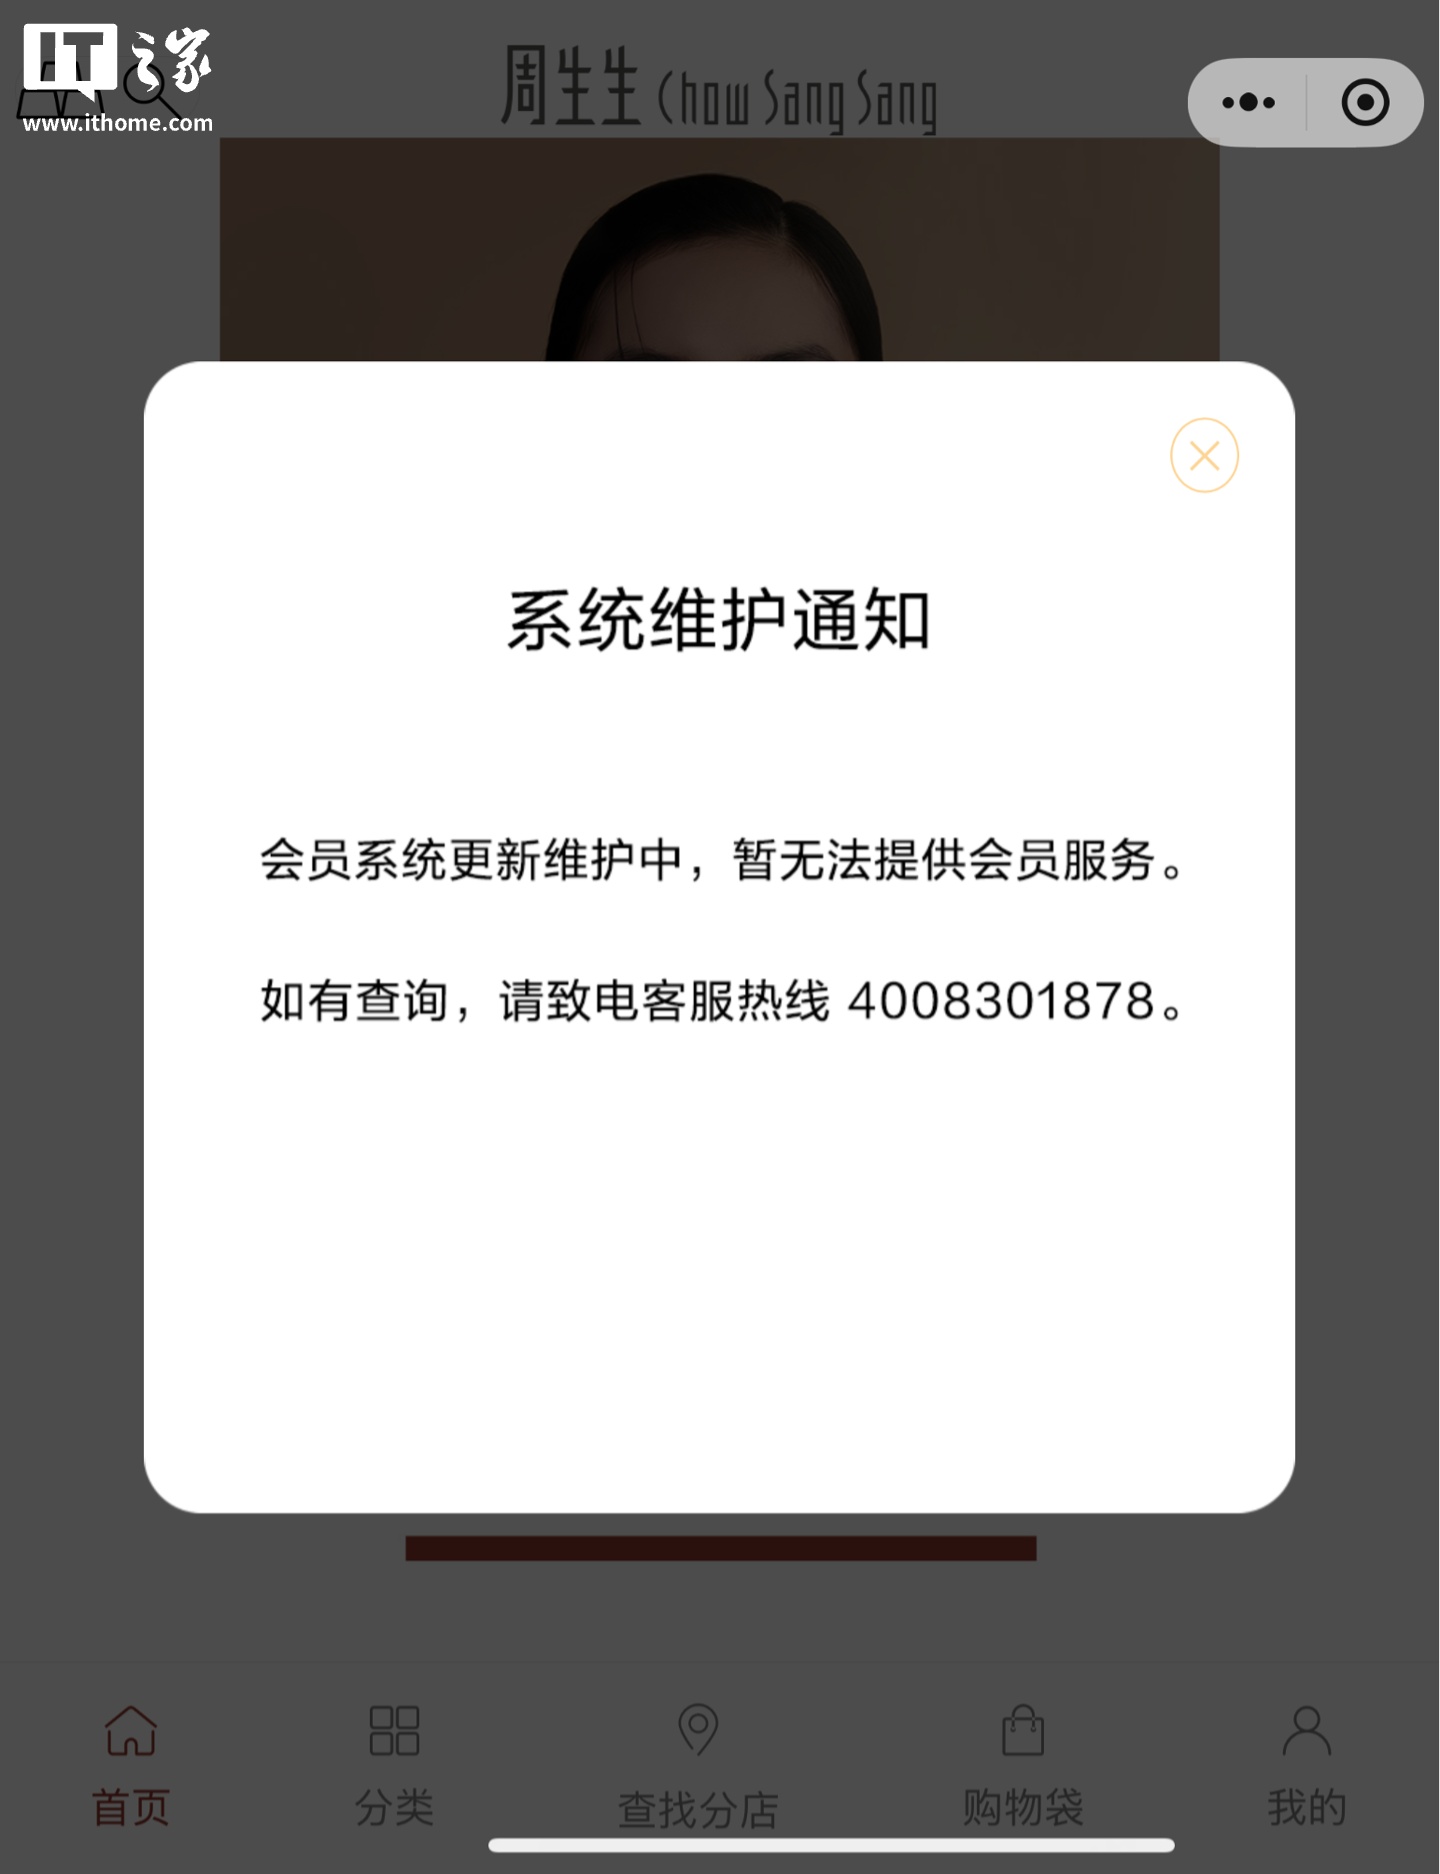
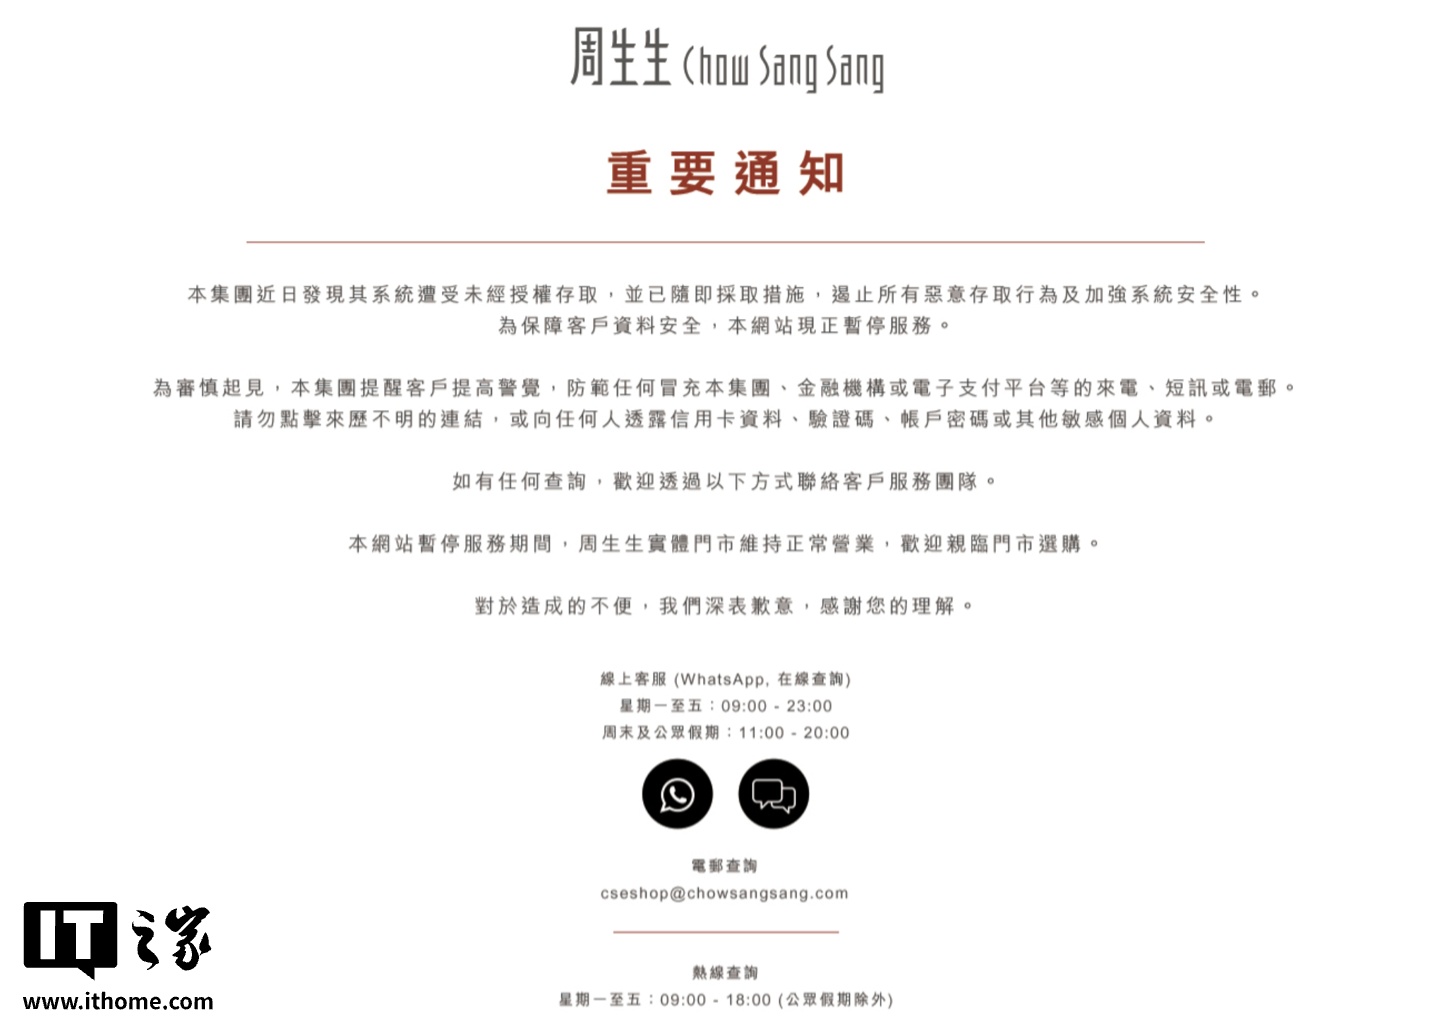
When IT Home reported the incident on November 14, 2026, Chow Sang Sang’s website was still unavailable. A notice on the site said service had been suspended to protect customer data. The company’s official shopping mini-program was also not working normally and displayed a message saying membership services were temporarily unavailable during a system update.